

Connect SharePoint with your own app
Summary
Section titled “Summary”This page is for IT and security teams. Some companies do not allow apps from other companies in their Microsoft 365. Those companies connect SharePoint to KonversAI with their own app. Your IT makes an app registration in your own Microsoft 365, gives it read access to one SharePoint folder, and enters its client ID and client secret in KonversAI. Your company owns the app. You see its sign-ins in your own logs, and you can turn it off at any time.
The result is the same as with the KonversAI app: KonversAI reads only the folders that you give it. For the KonversAI app, see Connect SharePoint.
Who can do this
Section titled “Who can do this”In KonversAI, a team member with the Modify tenant settings permission enters the app on the Import from SharePoint screen. A Tenant Admin has this permission, always.
In Microsoft 365, the person who runs the setup script needs the Global Administrator or the Privileged Role Administrator role, because the script gives admin consent to one permission. To give access to a folder, the person must also be an owner of the SharePoint site or a SharePoint administrator.
Before you start
Section titled “Before you start”- Install PowerShell 7 and the module Microsoft.Graph.Authentication:
Install-Module Microsoft.Graph.Authentication. - Copy the link of the SharePoint folder. Open the folder in SharePoint in your web browser and copy the address from the address bar.
- In KonversAI, select Knowledge in the left sidebar, then Imports, then New import. On the Start import screen, select SharePoint (preview). On the Import from SharePoint screen, select Use your own app.
Make the app with the setup script
Section titled “Make the app with the setup script”-
Download New-KonversAISharePointApp.ps1. Read it before you run it.
-
Run the script with the folder link. Add
-WhatIffirst to see what the script will do.Terminal window ./New-KonversAISharePointApp.ps1 -FolderUrl "<folder link>" -SecretMonths 12 -
In Microsoft: A Microsoft sign-in opens in your browser. The first time, Microsoft asks you to approve permissions for Microsoft Graph Command Line Tools. Approve them for yourself only. Do not select Consent on behalf of your organization.
-
The script does these four things in about one minute, in your own Microsoft 365. It sends nothing to KonversAI.
- It makes the app registration “KonversAI SharePoint”.
- It gives the app only the permission
Files.SelectedOperations.Selected, with admin consent. - It gives the app read access to the folder.
- It makes a client secret.
-
The script shows the folder link, the client ID, the client secret and the expiry date of the secret. Microsoft shows the secret one time only. If your company records PowerShell sessions, add
-SecretToClipboard: the script then copies the secret instead of showing it.
Enter the app in KonversAI
Section titled “Enter the app in KonversAI”-
In KonversAI: On the Import from SharePoint screen, in step 2, Enter the app details, enter the Folder link, the Application (client) ID, the Client secret value and the Secret expiry date. Select Save. KonversAI finds your Microsoft 365 from the folder link. KonversAI encrypts the secret, and nobody can see it again on this screen.
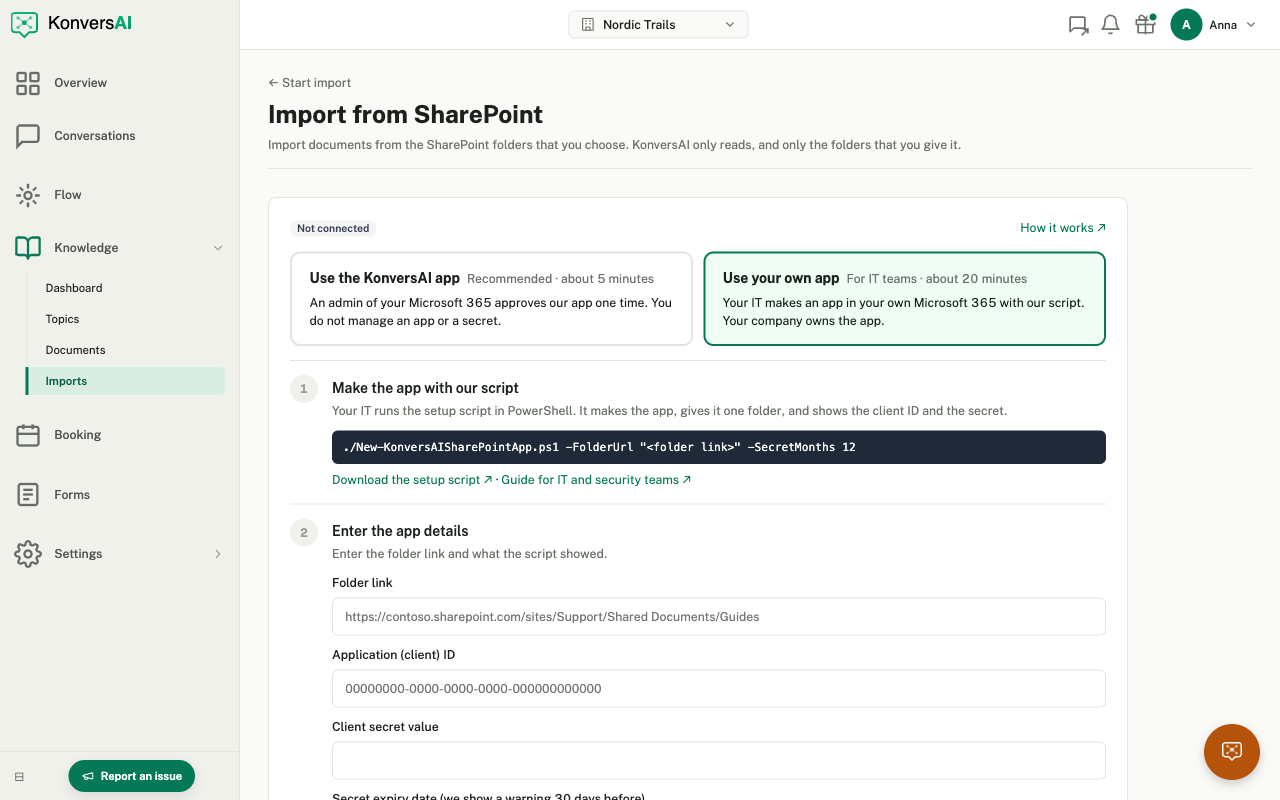
Use your own app: run the script, then enter what it shows.
-
In KonversAI: The screen shows Connected with your own app. Under Add a folder, paste the folder link in Folder link and select Check. The folder shows under Folders that KonversAI can read.
-
In KonversAI: Select Choose files next to the folder to choose the files. See Import documents from SharePoint.
To give your app access to more folders, run Grant-KonversAISharePointAccess.ps1 with the client ID of your app. Then, on the Import from SharePoint screen, add each folder under Add a folder with Check.
./Grant-KonversAISharePointAccess.ps1 -FolderUrl "<folder link>" -AppId <client ID>Make the app by hand
Section titled “Make the app by hand”If you prefer the Microsoft Entra admin center, do the steps of the script by hand. The result is the same.
- Open the Microsoft Entra admin center and go to Applications > App registrations > New registration.
- Name the app, for example “KonversAI SharePoint”. Select Accounts in this organizational directory only. Do not add a redirect URI. Select Register. Copy the Application (client) ID.
- Go to API permissions > Add a permission > Microsoft Graph >
Application permissions. Select
Files.SelectedOperations.Selectedand select Add permissions. Do not add other permissions. - Select Grant admin consent. With this permission alone, the app can read no files.
- Go to Certificates & secrets > Client secrets > New client secret. Choose an expiry date. Copy the Value at once, not the Secret ID.
- Give the app read access to the folder with
Grant-KonversAISharePointAccess.ps1
and
-AppId <client ID>. - Enter the app in KonversAI: on the Import from SharePoint screen, select Use your own app, then fill in Enter the app details and select Save.
Technical details for security teams
Section titled “Technical details for security teams”Permission
Section titled “Permission”The app has one Microsoft Graph application permission:
Files.SelectedOperations.Selected (ID bd61925e-3bf4-4d62-bc0b-06b06c96d95c).
Alone, this permission gives access to no files. The app can read only the
folders that you give to it, with the role “read”. The app has no delegated
permissions: no sign-in of your users, and no access to email, Teams, users or
other sites.
The setup scripts use the permissions of the person who runs them, through Microsoft’s own Microsoft Graph Command Line Tools. To remove those afterwards, go to Enterprise applications > Microsoft Graph Command Line Tools > Permissions.
Calls that KonversAI makes
Section titled “Calls that KonversAI makes”All calls are read-only, over HTTPS, from the KonversAI servers.
| Call | When and why |
|---|---|
GET https://login.microsoftonline.com/<name>.onmicrosoft.com/v2.0/.well-known/openid-configuration |
When you save, and before each import. KonversAI finds the directory ID of the SharePoint address, to make sure that the folder is in your Microsoft 365. Needs no sign-in. |
POST https://login.microsoftonline.com/<directory ID>/oauth2/v2.0/token |
KonversAI gets an app-only token for your directory with your client ID and secret. |
GET https://graph.microsoft.com/v1.0/shares/u!<encoded folder link>/driveItem |
KonversAI finds the folder from its link. |
GET https://graph.microsoft.com/v1.0/drives/<drive ID>/items/<item ID>/children |
KonversAI lists the files in the folder and its subfolders: when you start an import, and every hour after the import, to find new, changed and deleted files. |
GET https://graph.microsoft.com/v1.0/drives/<drive ID>/items/<file ID> |
KonversAI gets a short-lived download address for each file that you import, and for each new or changed file that the hourly sync finds. |
GET <download address> |
KonversAI downloads the file. KonversAI sends no token to this address. |
What KonversAI stores
Section titled “What KonversAI stores”- The client ID, the client secret (encrypted, never shown again), its expiry date, your directory ID, and the folder links that KonversAI could read.
- For each import: the path, size, date, version and SharePoint address of each file, and the text of the files that you import, as knowledge documents. Only team members see the SharePoint address, in the KonversAI console. The assistant does not show it to the people who chat with it.
KonversAI does not store the files themselves, and it never writes to SharePoint.
Your control
Section titled “Your control”- See every sign-in of the app in Microsoft Entra: Enterprise applications > your app > Sign-in logs > Service principal sign-ins.
- To stop at once, delete the client secret or the app.
- To remove one folder, run Grant-KonversAISharePointAccess.ps1 with
-Revokeand-AppId <client ID>.
Change the client secret
Section titled “Change the client secret”The client secret of your app expires, usually after 6 to 24 months. KonversAI shows a warning on the Import from SharePoint screen 30 days before the expiry date that you entered. When the secret expires, KonversAI cannot read SharePoint, and the hourly sync no longer updates the documents.
- In Microsoft: In your app, make a new client secret under Certificates & secrets.
- In KonversAI: On the Import from SharePoint screen, open Change the app details. Enter the Folder link, the new Client secret value and the new Secret expiry date. Select Save.
- In Microsoft: Delete the old client secret.
Why would we use our own app and not the KonversAI app?
Section titled “Why would we use our own app and not the KonversAI app?”Use your own app when your company does not allow apps from other companies in its Microsoft 365, or when your security team wants the app, its secret and its sign-in logs in your own directory. The access to SharePoint is the same: read access to the folders that you give, and nothing else.
Does the setup script send anything to KonversAI?
Section titled “Does the setup script send anything to KonversAI?”No. New-KonversAISharePointApp.ps1 works only in your own Microsoft 365. It shows the client ID and the client secret on your screen. You enter them in KonversAI yourself.
Which permission does our own app need?
Section titled “Which permission does our own app need?”Only the Microsoft Graph application permission
Files.SelectedOperations.Selected, with admin consent. Do not add other
permissions. Alone, this permission gives access to no files.
What happens when the client secret expires?
Section titled “What happens when the client secret expires?”When the client secret expires, KonversAI cannot read SharePoint. New imports fail, and the hourly sync no longer updates the documents. Documents that you imported stay in the knowledge base. Make a new secret and enter it under Change the app details on the Import from SharePoint screen. KonversAI shows a warning 30 days before the expiry date that you entered.
How do we see what KonversAI does with our app?
Section titled “How do we see what KonversAI does with our app?”In Microsoft Entra, go to Enterprise applications > your app > Sign-in logs > Service principal sign-ins. Every token that KonversAI gets shows there.
Can we use a renamed SharePoint address?
Section titled “Can we use a renamed SharePoint address?”Not yet. KonversAI finds your Microsoft 365 from the SharePoint address. If KonversAI shows “We could not find the Microsoft 365 of this SharePoint address”, contact KonversAI support.
Last reviewed . Tell us when a step no longer matches the product.